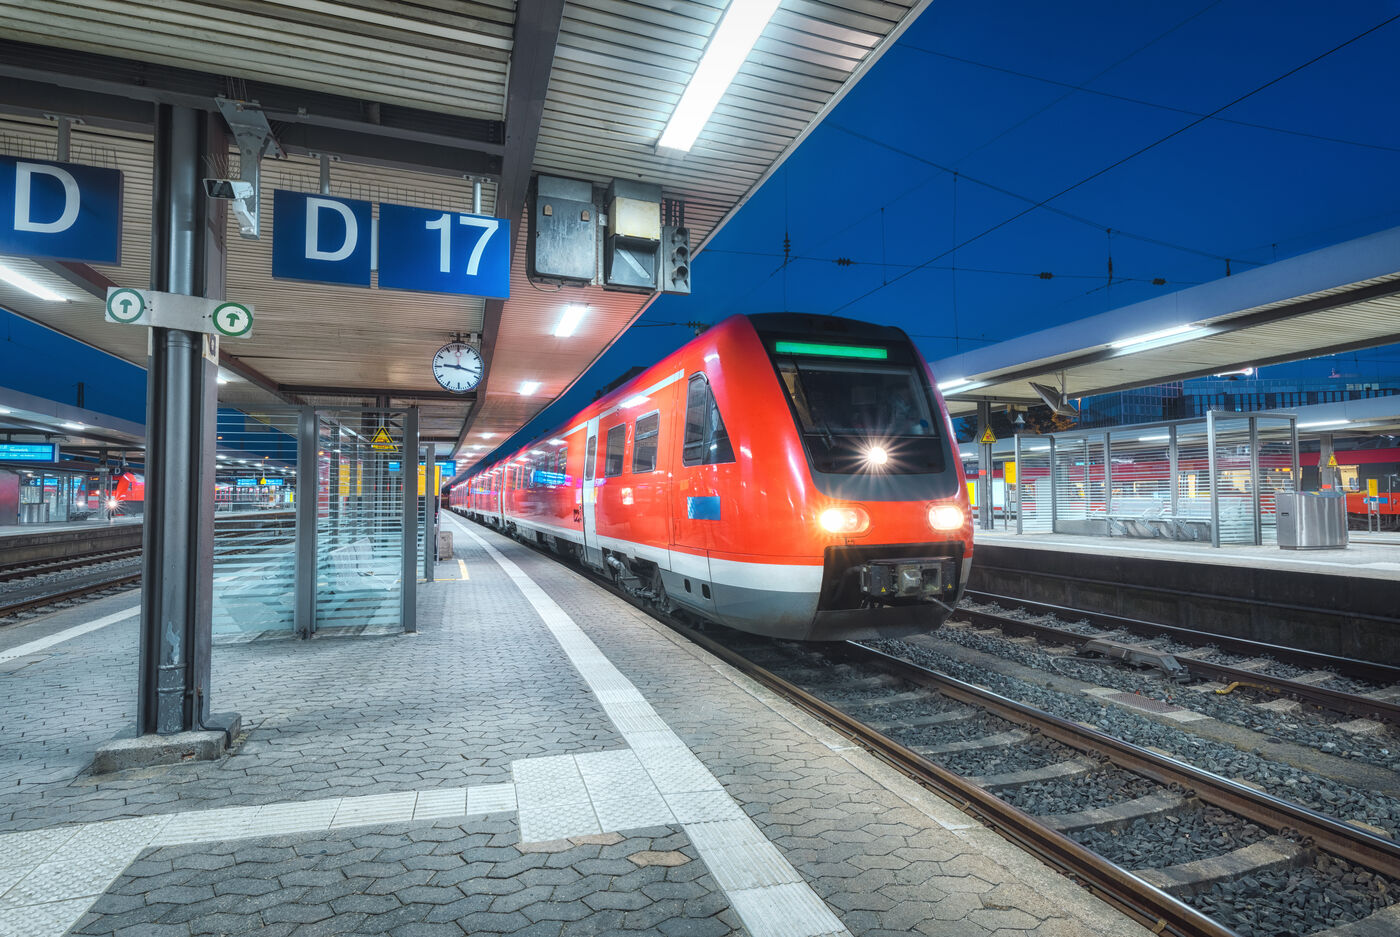
Detecting threats before they spread
Early detection of threats
Threats and faults can remain hidden across hundreds of on-board systems. Continuous detection and clear alerts help engineering and security teams investigate early, before an issue spreads or disrupts service. Learn more about Delta intrusion detection.
Solution
Three products cover detection in depth. Delta learns each system's normal behaviour and alerts on deviation, with no signature database to keep updated. Echo reports the availability and configuration of every on-board system, helping reveal failed or misconfigured devices. Security Gateway filters traffic between network zones and alerts on unauthorised access attempts at the boundary. Alerts from all three arrive in Dashboard, where your own teams can review and triage them. RazorSecure analyst triage is available where included in a managed service.
Across the portfolio, RazorSecure products protect more than 3,200 rail vehicles in service.
Delta: early detection and real-time insights
Visibility across the entire fleet Delta is an Intrusion Detection System (IDS). It monitors the network and detects threats continuously across your entire fleet.
Broader monitoring coverage helps reduce security blind spots.
Continuous monitoring for suspicious behaviour Delta checks network activity for suspicious behaviour continuously, so your team can respond early, before a threat spreads.
Early investigation helps reduce the risk of threats developing into costly outages or safety-related incidents.
Anomaly detection on the vehicle Delta processes data on the vehicle continuously, connected or not. When behaviour deviates from the baseline, it creates an event on the vehicle and forwards it to shore when connected.
Local detection continues without constant cellular connectivity, helping protect assets in disconnected environments.
Echo: centralised monitoring and streamlined management
One view of hundreds of systems Echo simplifies the monitoring of hundreds of on-board IT and OT systems. It identifies configuration mismatches and performance issues that could hide vulnerabilities.
A common view across suppliers reduces the effort of coordinating maintenance workflows.
System availability and device health See system availability and device health in one view, regardless of train type or vendor.
Proactive health monitoring helps teams protect availability and meet service commitments.
Faster fault resolution Echo helps your engineers find and fix problems faster, so fix times improve and systems stay stable.
Faster fault resolution supports vehicle availability and scheduled services.
Security Gateway: network segmentation and real-time alerts
Network segmentation and security controls Security Gateway uses a Layer 7 firewall with specialist rail protocol support. It enforces network segmentation and filters malicious traffic on both new and legacy fleets.
Boundary filtering helps protect critical train systems and supports the continued use of existing assets.
Alerts on unauthorised access Real-time alerts on unauthorised access attempts let your team respond fast.
Clear alerts help shorten incident-response times and limit disruption.
Protocol filtering at security-zone boundaries Security Gateway applies Layer 7 and rail-protocol filtering to traffic crossing between security zones. Pair it with Delta for visibility of devices and traffic within the zones.
Enforced network separation supports the evidence needed for applicable security requirements.
How this fits The Secure Train
Secure Train is the wider rolling stock architecture behind these challenges: enforced zoning, passive detection, secure maintenance, asset visibility and one operational picture.
Explore Secure TrainPlan the controls together
Map the fleet’s requirements to network boundaries, detection coverage and maintenance access. Secure Train shows how those controls fit together.
Related challenges
Separating critical on-board networks
Network segmentation that protects both new and legacy fleets.
Controlling maintenance and insider access
Controlled maintenance access and audit records that reduce insider risk.
Meeting NIS2 and TS 50701 obligations
What TS 50701, IEC 62443 and national rules require, and how to meet them.
Knowing what is really on your trains
A live inventory of every device and configuration on every train.
Connecting legacy fleets safely
How to secure older fleets that were built before cyber security standards existed.